


See Wallarm's AI Control Platform In Action
Kubernetes API Security
Wallarm runs natively in Kubernetes as an Ingress controller, a sidecar, an Istio filter, or an out-of-band eBPF sensor. It inventories every API endpoint and blocks OWASP API Top 10 attacks, bots, and abuse without manual rules.
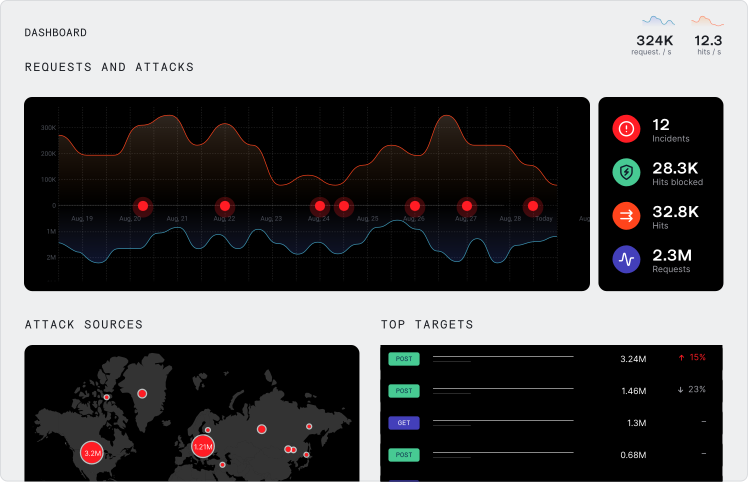
The world's most demanding teams run on Wallarm.


What is Kubernetes API security?
Kubernetes API security is the practice of discovering, testing, and protecting the APIs exposed by workloads in a Kubernetes cluster. It covers ingress (north-south) traffic entering the cluster and service-to-service (east-west) calls between microservices. It differs from securing the Kubernetes control plane itself, which is handled by RBAC, admission control, and pod security.
Securing cloud-native APIs in Kubernetes
Wallarm protects APIs and microservices in any cluster with no manual rule configuration and ultra-low false positives.

Discover every in-cluster API
Automatically inventory MCP, REST, GraphQL, gRPC, and SOAP-XML across namespaces, with no Swagger or schema upload.

Protect east-west traffic
Inspect service-to-service calls, where BOLA, broken authentication, and lateral movement happen.

Block the OWASP API Security Top 10 (2023)
Stop BOLA, broken authentication, SSRF, and unrestricted resource consumption, plus injection, XXE, and RCE.

Stop bots, account takeover, and L7 DDoS
Mitigate credential stuffing, account takeover, and application-layer denial of service in real time.

Kubernetes-native operations
Deploy with Helm, configure with pod annotations and labels, and scale with your replicas.

Any cloud, any cluster
Run on EKS, GKE, AKS, OpenShift, and self-managed clusters in private data centers.
How to deploy Wallarm in Kubernetes
Choose the mode that fits your cluster. Every option is installed with Helm and managed from the same Wallarm Console.
| Mode | Best for | Traffic covered | Blocking |
|---|---|---|---|
| NGINX Ingress Controller | Clusters that use NGINX at the edge | North-south | Inline |
| Kong Ingress Controller | Clusters that use Kong | North-south | Inline |
| Sidecar proxy | Zero-trust, per-pod protection; works with any Ingress controller, including AWS ALB | North-south and east-west | Inline |
| Istio filter | Service mesh environments | Mesh traffic | Inline and Out-of-Band |
| eBPF sensor | Visibility with no change to the traffic path | Inbound traffic only (including service-to-service) | Out-of-band (detect and alert) |
Replacing Ingress NGINX?
Keep your API security.
The Kubernetes community has retired the Ingress NGINX project, and it no longer receives security fixes. Wallarm's Ingress Controller now runs on the actively maintained F5 NGINX Ingress Controller, and a step-by-step migration guide covers the move. Moving to Istio or another Envoy-based gateway? The Wallarm connector for Istio and Envoy keeps protection in place. The Kong connector works with Ingress and Gateway API routes, and the Wallarm Sidecar runs behind any Ingress controller.
Built for how Kubernetes teams operate
At the foundation of the Wallarm design ethos is privacy, flexibility and performance.
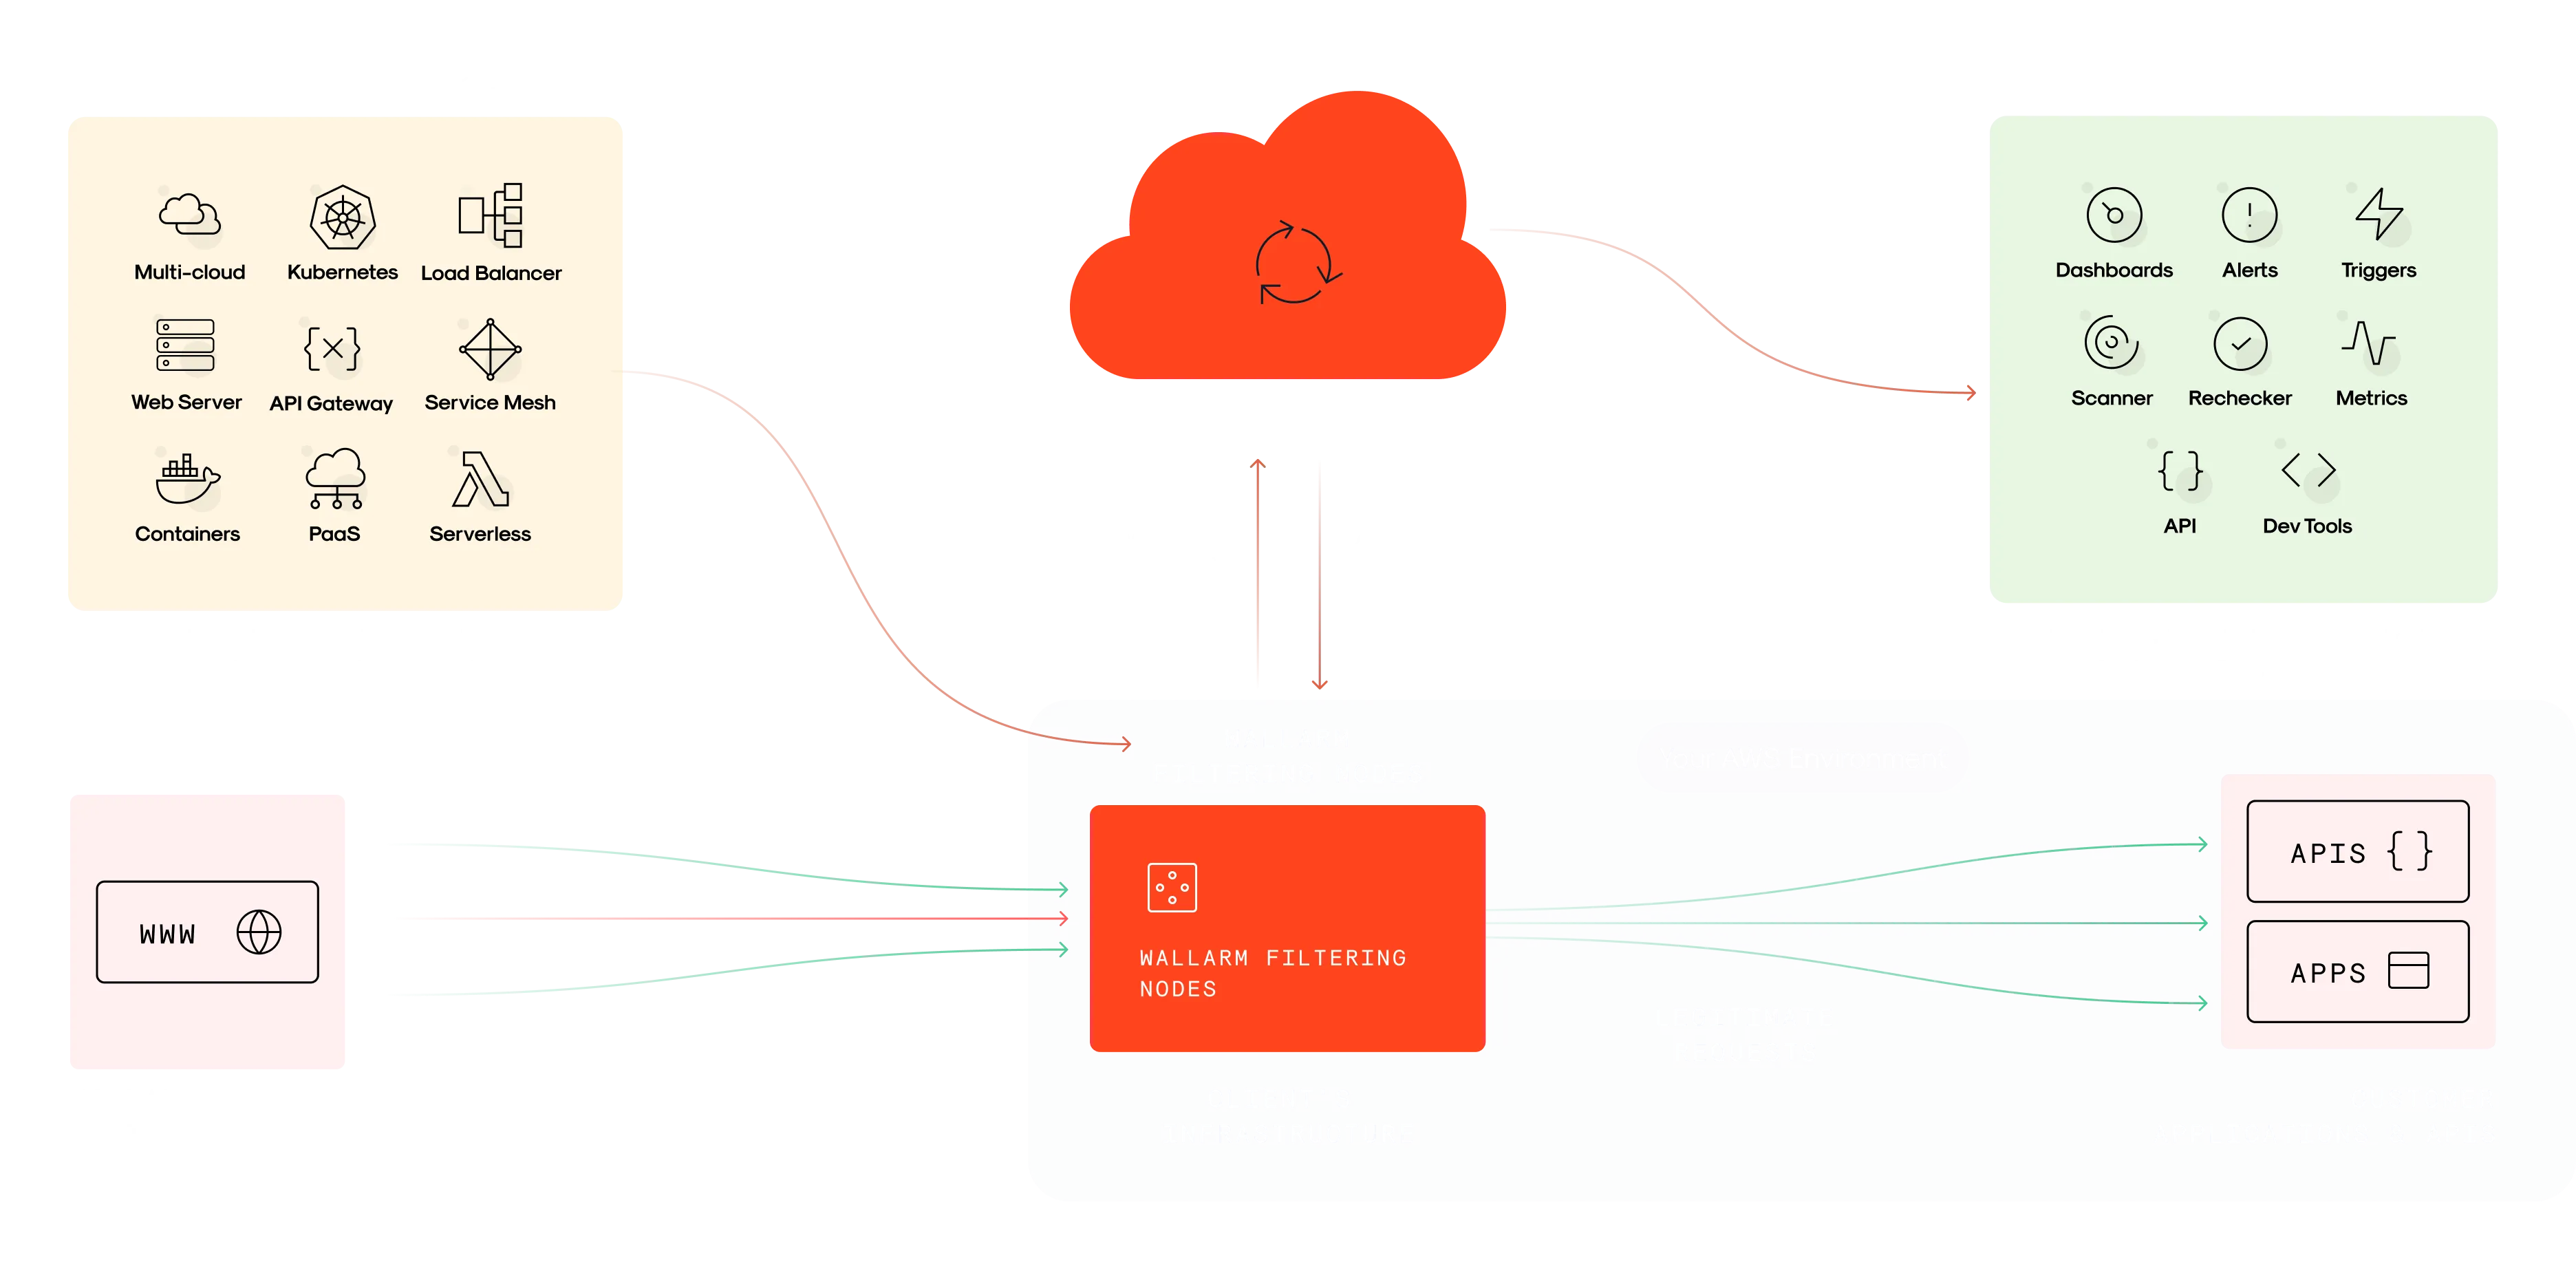
Inline deployment of our hybrid SaaS solution involves two main components: server-side software that deploys in your infrastructure within minutes and our powerful cloud-hosted analytics backend.
Privacy
Traffic is analyzed inside your cluster. Only statistics, API structure, and the details of malicious requests reach the Wallarm Cloud, and you can mask sensitive values before they leave.
Flexibility
Run inline or out-of-band, and protect a whole cluster, a namespace, or a single pod.
Performance
The filtering node adds 0.05ms of latency at 1700 requests per second.
Securing AI workloads in Kubernetes
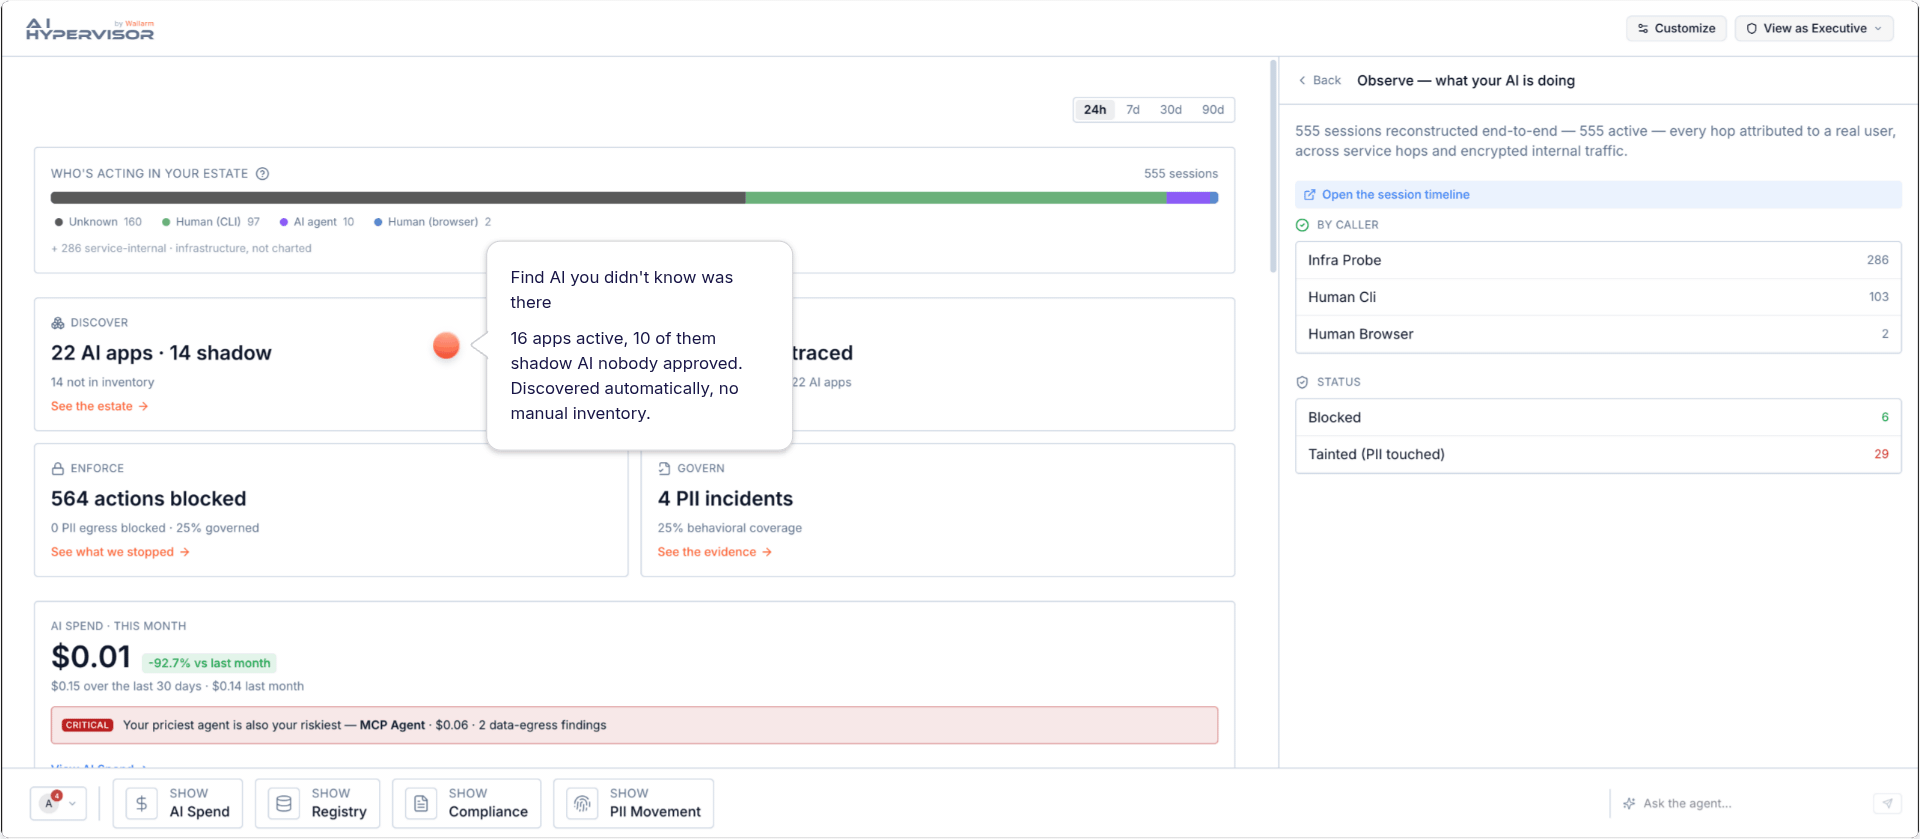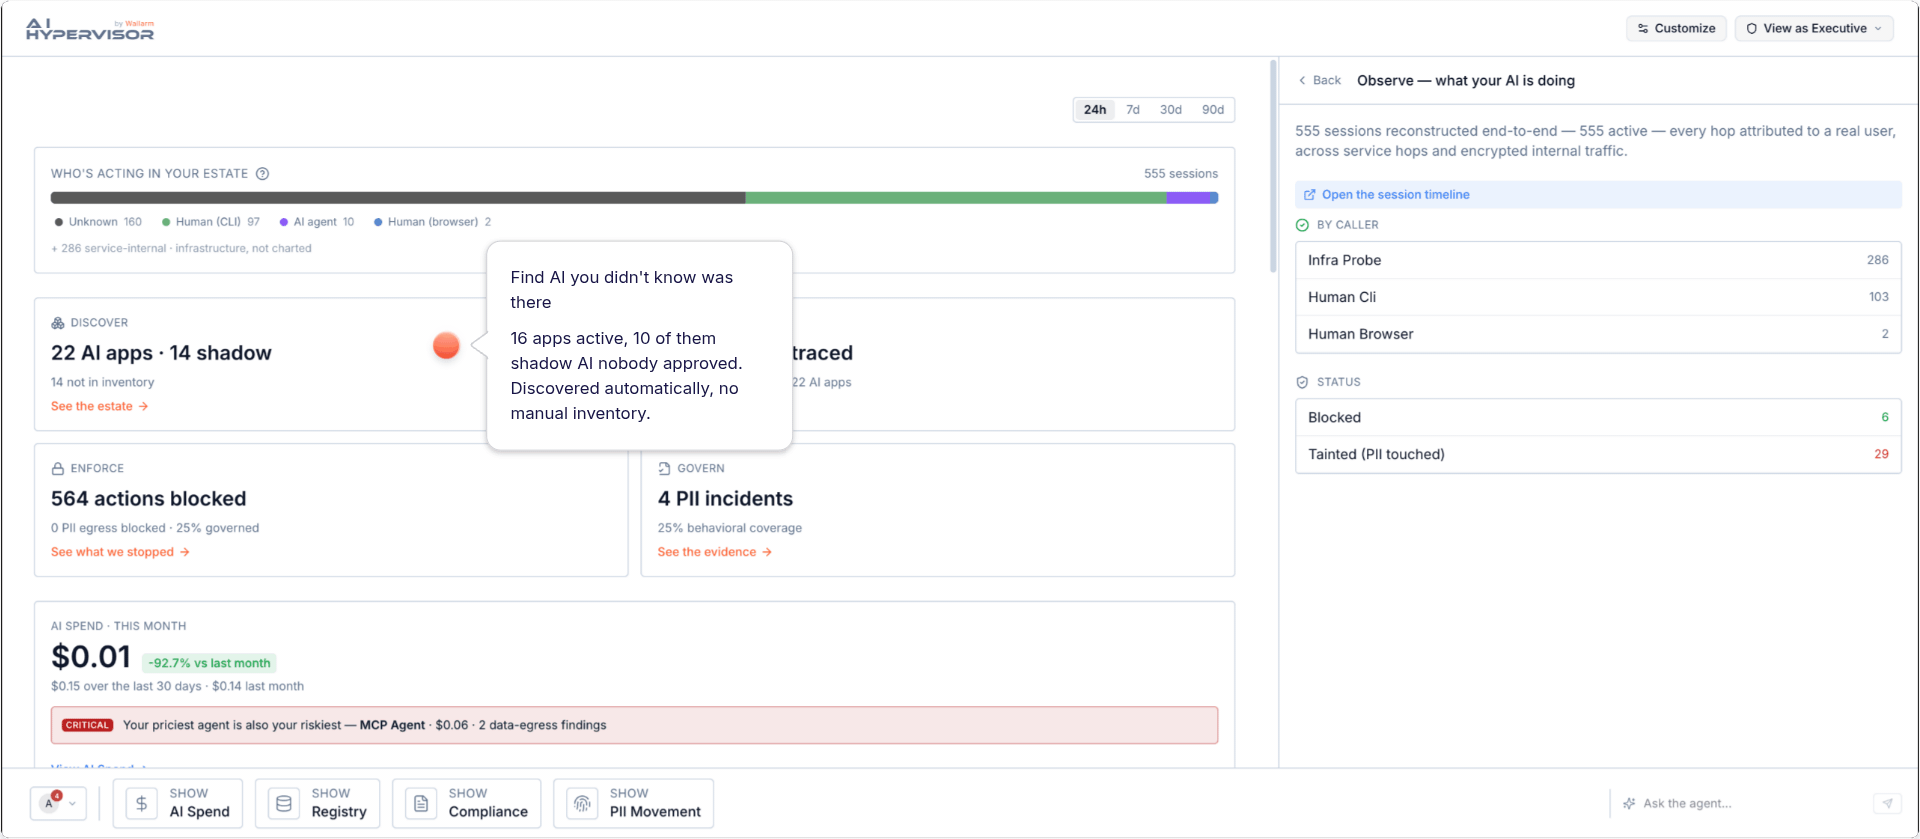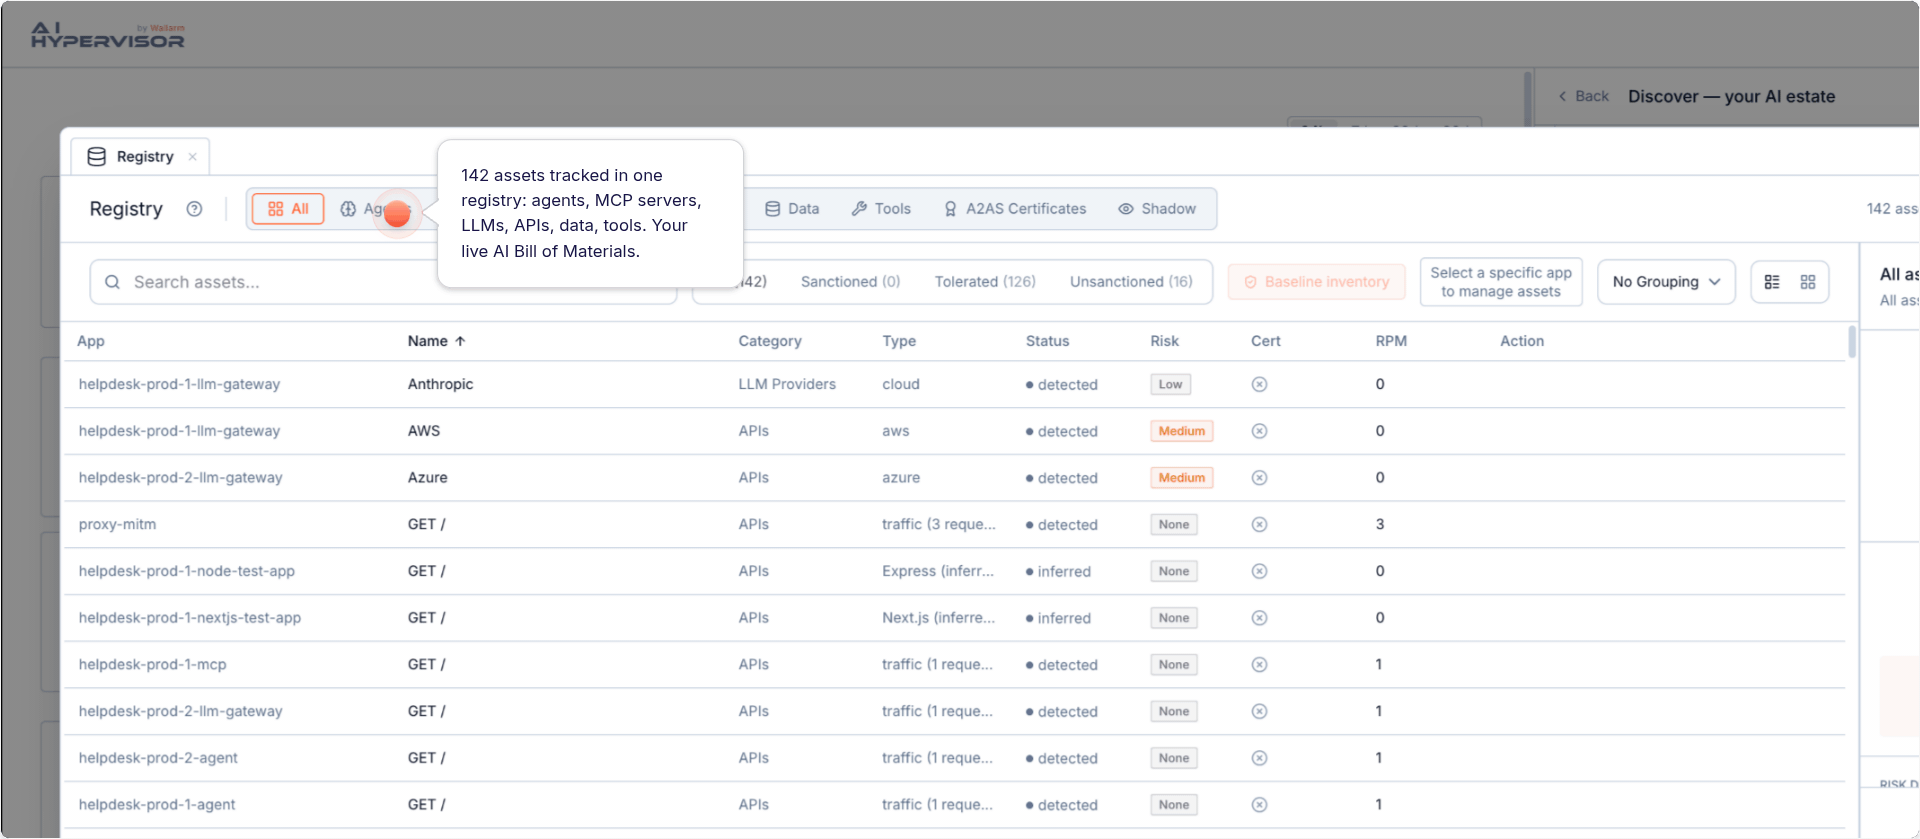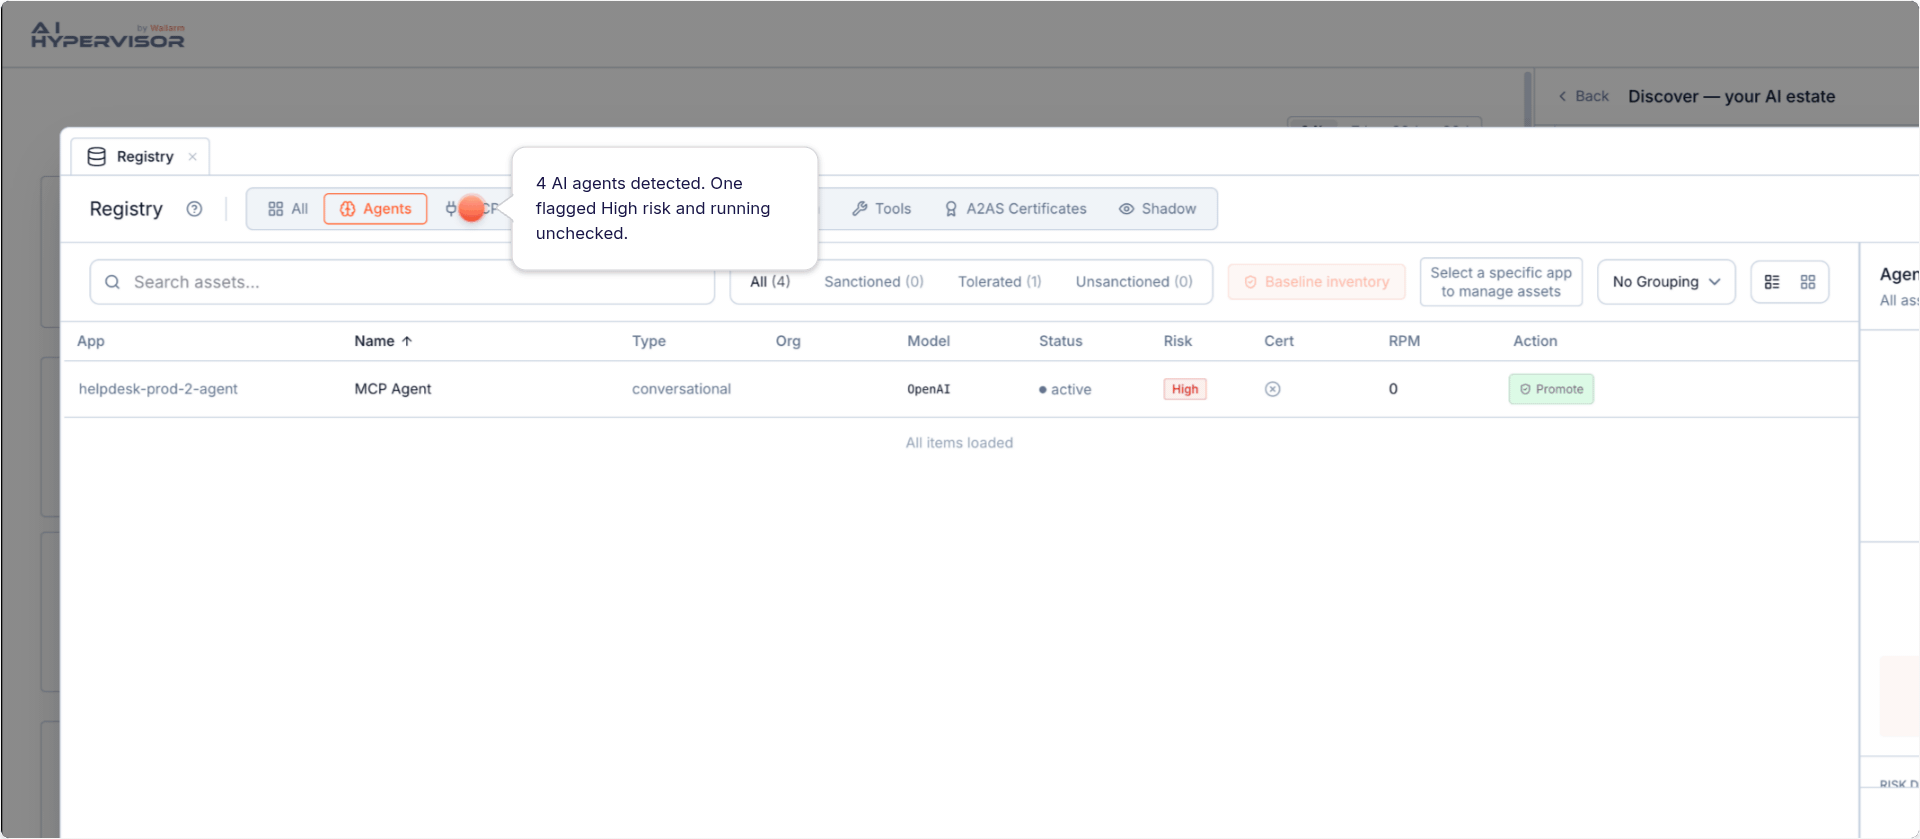
LLM gateways, MCP servers, and AI agents increasingly run as Kubernetes services and call your internal APIs. Wallarm's AI Hypervisor extends the same in-cluster visibility to AI traffic, mapping which agents call which APIs and enforcing data boundaries.
Frequently asked questions
What is Kubernetes API security?
Kubernetes API security is the practice of discovering, testing, and protecting the APIs exposed by workloads in a Kubernetes cluster, covering both ingress traffic and service-to-service calls.
How is Kubernetes API security different from Kubernetes security?
Kubernetes security protects the cluster itself through RBAC, pod security, image scanning, and the Kubernetes API server. Kubernetes API security protects the application APIs your workloads expose, which is where business-logic attacks like BOLA happen.
Does Wallarm protect east-west traffic between microservices?
Yes. The sidecar deployment inspects traffic to each pod, including internal calls, and the eBPF sensor observes all in-cluster traffic out-of-band.
Can Wallarm run without changing my traffic path?
Yes. The eBPF deployment observes traffic out-of-band, so it detects attacks and discovers APIs without sitting inline.
Does Wallarm work with Istio, Kong, or AWS ALB?
Yes. Wallarm has an Istio filter and a Kong Ingress Controller connector, and the sidecar works behind any Ingress controller, including AWS ALB.
Which Kubernetes distributions does Wallarm support?
Wallarm runs on EKS, GKE, AKS, OpenShift, and self-managed clusters.
What should I do about the Ingress NGINX retirement?
The community Ingress NGINX project is retired and no longer receives security fixes, so plan a move to a maintained option. To stay on NGINX, migrate to the Wallarm Ingress Controller based on the F5 NGINX Ingress Controller. If you're moving to Istio or another Envoy-based gateway, use the Wallarm connector for Istio and Envoy. If you use Kong, the Wallarm connector for Kong Ingress Controller keeps protection in place. The Wallarm Sidecar works behind any Ingress controller.