

Privacy settings
We use cookies and similar technologies that are necessary to run the website. Additional cookies are only used with your consent. You can consent to our use of cookies by clicking on Agree. For more information on which data is collected and how it is shared with our partners please read our privacy and cookie policy: Cookie policy, Privacy policy
We use cookies to access, analyse and store information such as the characteristics of your device as well as certain personal data (IP addresses, navigation usage, geolocation data or unique identifiers). The processing of your data serves various purposes: Analytics cookies allow us to analyse our performance to offer you a better online experience and evaluate the efficiency of our campaigns. Personalisation cookies give you access to a customised experience of our website with usage-based offers and support. Finally, Advertising cookies are placed by third-party companies processing your data to create audiences lists to deliver targeted ads on social media and the internet. You may freely give, refuse or withdraw your consent at any time using the link provided at the bottom of each page.
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.

See Wallarm's AI Control Platform In Action
Talk to an Expert
Replace your legacy WAF with a platform
built for modern applications
built for modern applications
The unified WAAP platform built for modern applications.
Secure web applications, APIs, and AI through a single platform that delivers runtime visibility, protection, and governance. Unlike legacy WAFs, Wallarm was designed to secure today's application landscape.
AWS Security Competency
Available on AWS Marketplace
Patented TEchnology
Trusted By
The world's most demanding teams run on Wallarm.


Your applications changed. Your WAF didn't
APIs, AI, and Web Apps now run together.
Legacy security tools protect them separately.
Market
30+%
of the increase in API demand will come from AI and LLM-enabled applications
Source: Gartner
Gap
24%
of developers design APIs for AI agents, even though 89% use AI daily work.
Source: Postman 2025 State of the API Report
Detection
51%
of developers say their top security concern is unauthorized or excessive API calls from AI agents.
Source: Postman 2025 State of the API Report
Disconnected point products leave siloed tools, fragmented visibility, and incomplete governance. One platform closes the gaps.
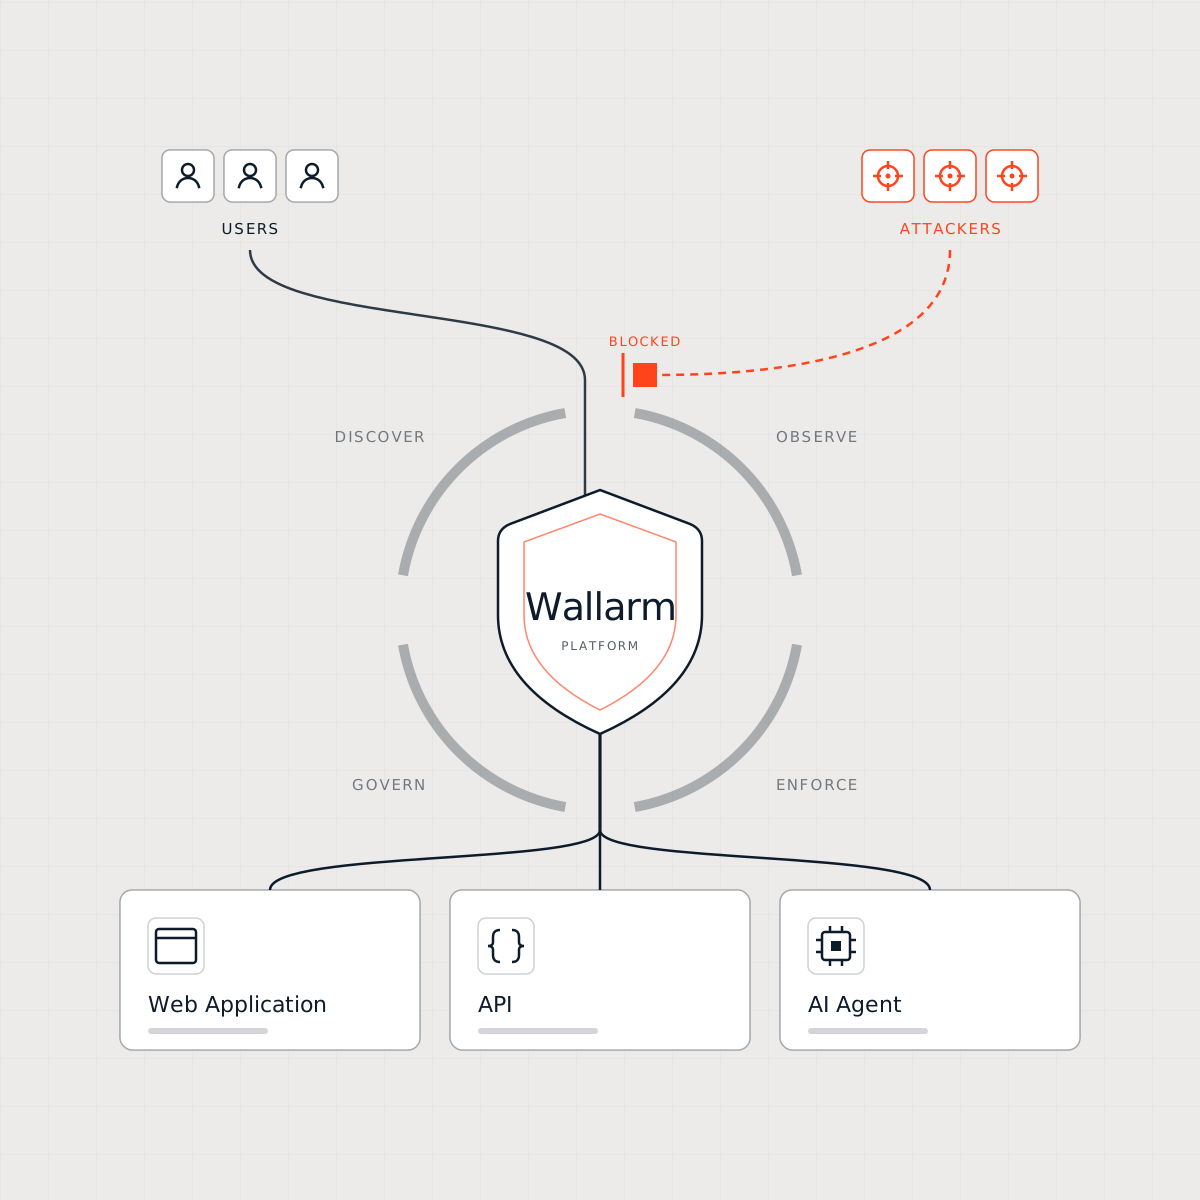
How the Wallarm platform works
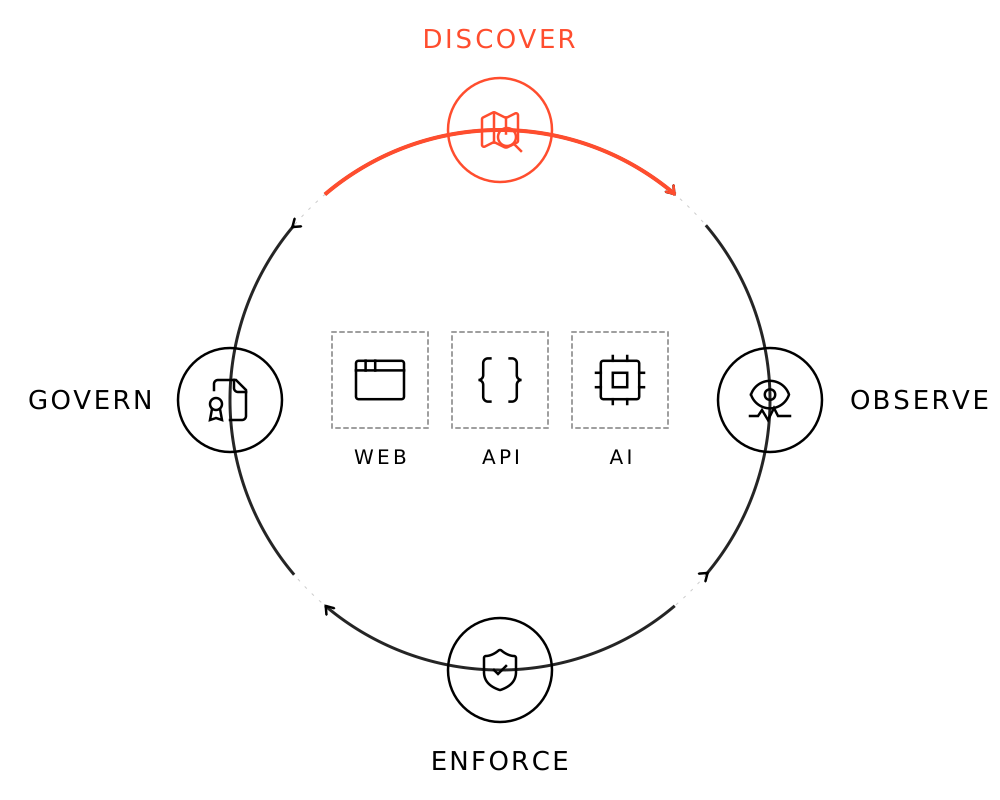
Discover. Observe. Enforce. Govern.
Across API, AI, and web.
Modern applications span API, AI, and web, but security solutions remain fragmented. Wallarm unifies them in a single platform with shared visibility, protection, and governance.
1
Discover
Maintain a complete, continuously updated inventory of your web applications, APIs, AI systems, and supporting infrastructure.
2
Observe
Understand how web applications, APIs, and AI interact with users, data, and services through continuous runtime visibility.
3
Enforce
Stop attacks, prevent sensitive data exposure, and reduce risk by applying consistent security policies across web applications, APIs, and AI systems.
4
Govern
Demonstrate security, compliance, and operational governance with centralized reporting, policy management, and continuous audit-ready evidence.
Four products. Every layer covered.
WAAP
Enforce
Replace your legacy WAF with protection built for modern applications. Wallarm reads the whole request instead of scanning for known-bad patterns, stopping disguised attacks on web apps and APIs without blocking real customers.
API Security
Discover
Enforce
Discover your APIs and block attacks against them in one product, one deployment, one console. Covers REST, GraphQL, gRPC, SOAP, and WebSocket, including the APIs behind your AI applications and agents.
AI Hypervisor
Discover
Observe
Enforce
Govern
Kernel-level runtime enforcement for AI. Observes every AI agent decision, enforces policy at the connection level, and generates continuous compliance evidence without modifying the application.
Infrastructure Discovery
Discover
Observe
Cross-account visibility across your entire AWS estate. Maps your cloud assets and AI workloads, surfaces shadow AI within minutes of deployment, and identifies paths attackers might take to your crown jewels.
Why our detection engine wins
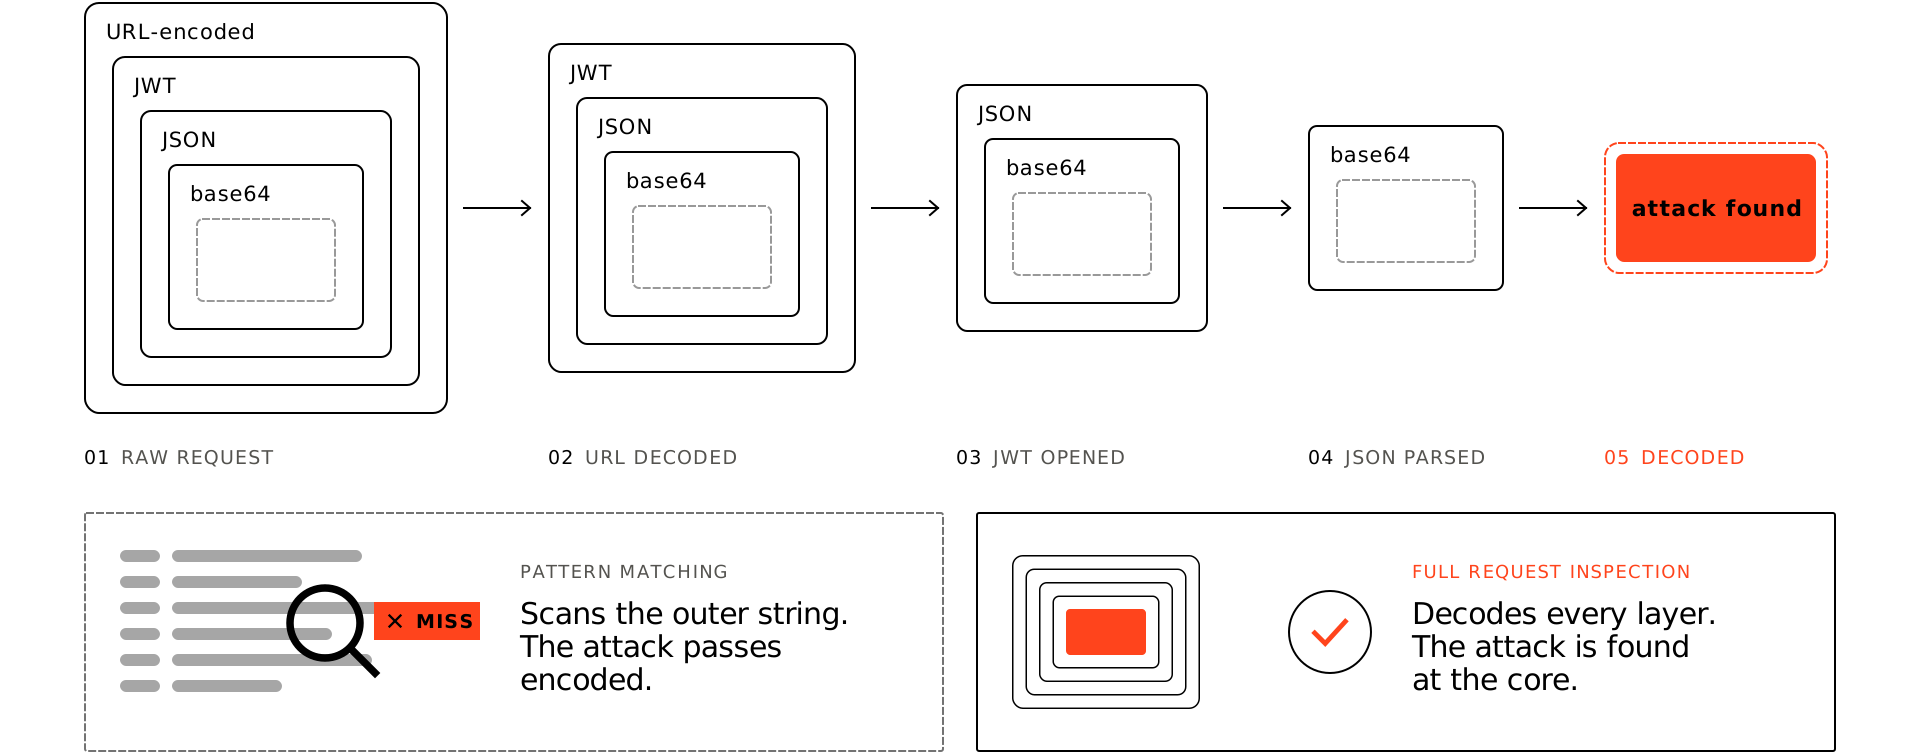
We parse and decode. Legacy WAFs pattern match.
Almost every legacy WAF keeps a list of known bad text patterns and matches requests against it. Attackers bypass that every day by obfuscating the attack. Wallarm takes the disguise off first, then checks whether the parts add up to an attack.
Obfuscation doesn’t work
Wallarm unwraps and decodes every request layer before analysis, so encoding tricks that pass pattern-matching firewalls don't get through.
No size limit to hide behind
Many WAFs stop reading after a fixed number of kilobytes, and attackers hide payloads past that point. Wallarm has no size cutoff, so padding doesn't help them.
Built for modern protocols
Wallarm parses GraphQL, gRPC, SOAP, and WebSocket traffic, and inspects JWTs, so attacks hidden inside modern API formats don't pass as raw text.
Blocks the attacker, not your customers
Most firewalls block by IP address, which attackers rotate and which can lock out legitimate users on a shared network. Wallarm blocks the malicious session and lets everyone else through.
Industries
Built for the applications that run your revenue.
Payments and fintech
Every transaction is an API call, so an attack on the API is an attack on the money. We block the attack without blocking real payments.
Retail and ecommerce
The storefront is software now: checkout, mobile app, loyalty program. We stop fraud and abuse without blocking real shoppers at peak traffic.
Banking
Regulators now ask how connections to outside apps are protected. We give you evidence you can show a regulator.
AWS Security Competency
Built for AWS.
Deploys wherever your applications run.
GuardDuty detects. IAM Access Analyzer flags. Security Hub aggregates. None were built to see what your web applications, APIs, and AI agents are actually doing at runtime. Wallarm closes that gap natively, inside your AWS environment, and makes the AWS security services you already pay for more effective.
A single Wallarm deployment connects your existing AWS security stack (Security Hub, GuardDuty, IAM Access Analyzer, Inspector, Macie, and more) so the investments you've already made work together to protect your applications, APIs, and AI infrastructure. Enforcement runs inside your own VPC, keeping traffic in your environment. Discovery uses cross-account IAM role assumption with no stored credentials, so you get visibility across accounts without new security risk.
A single Wallarm deployment connects your existing AWS security stack (Security Hub, GuardDuty, IAM Access Analyzer, Inspector, Macie, and more) so the investments you've already made work together to protect your applications, APIs, and AI infrastructure. Enforcement runs inside your own VPC, keeping traffic in your environment. Discovery uses cross-account IAM role assumption with no stored credentials, so you get visibility across accounts without new security risk.
Security Competency
Application Security

Marketplace
Available now · Private offers & co-sell
Three Deploy Modes
Self-managed open-source edge inside your VPC. Security Edge in-VPC. Security Edge SaaS. Choose what fits your trust boundary.
Findings → Actions
GuardDuty and Security Hub findings land on the Wallarm topology graph with full AI runtime context — in plain language your team can act on.
Certified AWS Security
Validated against AWS's own AI security criteria. Surfaces over-permissioned AI agent roles with what those permissions actually reach.
Built for the whole leadership team
Different Roles. Different Stakes.
One Shared Responsibility.
For the CIO
Your applications now span web, APIs, and AI, and your security tools are still separate point products. Wallarm unifies them in one WAAP platform, so you reduce complexity and adopt AI with confidence, without the liability of unmanaged risk.
For the CISO
Your legacy WAF can't see your APIs or AI, and your team has stopped trusting its alerts. Wallarm reads the full request, shows you what's running across web, API, and AI, and blocks attacks before the next finding becomes a breach.
For the CTO
Engineering ships web apps, APIs, and AI faster than security can track. Wallarm deploys inline, out-of-band, as a sidecar, or in Kubernetes, and tests your APIs in the pipeline, so protection keeps up with release velocity.
Wallarm is the Leader
in API Security
Don't just take it from us. Read what security leaders and practitioners think about our platform.


"Application Security Umbrella for your company"
If You Can't See AI,
You Can't Secure It.
Wallarm gives you runtime visibility, protection, and governance across your web applications, APIs, and AI systems, so nothing operates outside your control.