

Privacy settings
We use cookies and similar technologies that are necessary to run the website. Additional cookies are only used with your consent. You can consent to our use of cookies by clicking on Agree. For more information on which data is collected and how it is shared with our partners please read our privacy and cookie policy: Cookie policy, Privacy policy
We use cookies to access, analyse and store information such as the characteristics of your device as well as certain personal data (IP addresses, navigation usage, geolocation data or unique identifiers). The processing of your data serves various purposes: Analytics cookies allow us to analyse our performance to offer you a better online experience and evaluate the efficiency of our campaigns. Personalisation cookies give you access to a customised experience of our website with usage-based offers and support. Finally, Advertising cookies are placed by third-party companies processing your data to create audiences lists to deliver targeted ads on social media and the internet. You may freely give, refuse or withdraw your consent at any time using the link provided at the bottom of each page.
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.

See Wallarm's AI Control Platform In Action
Tools
Application Security Stack Audit Kit
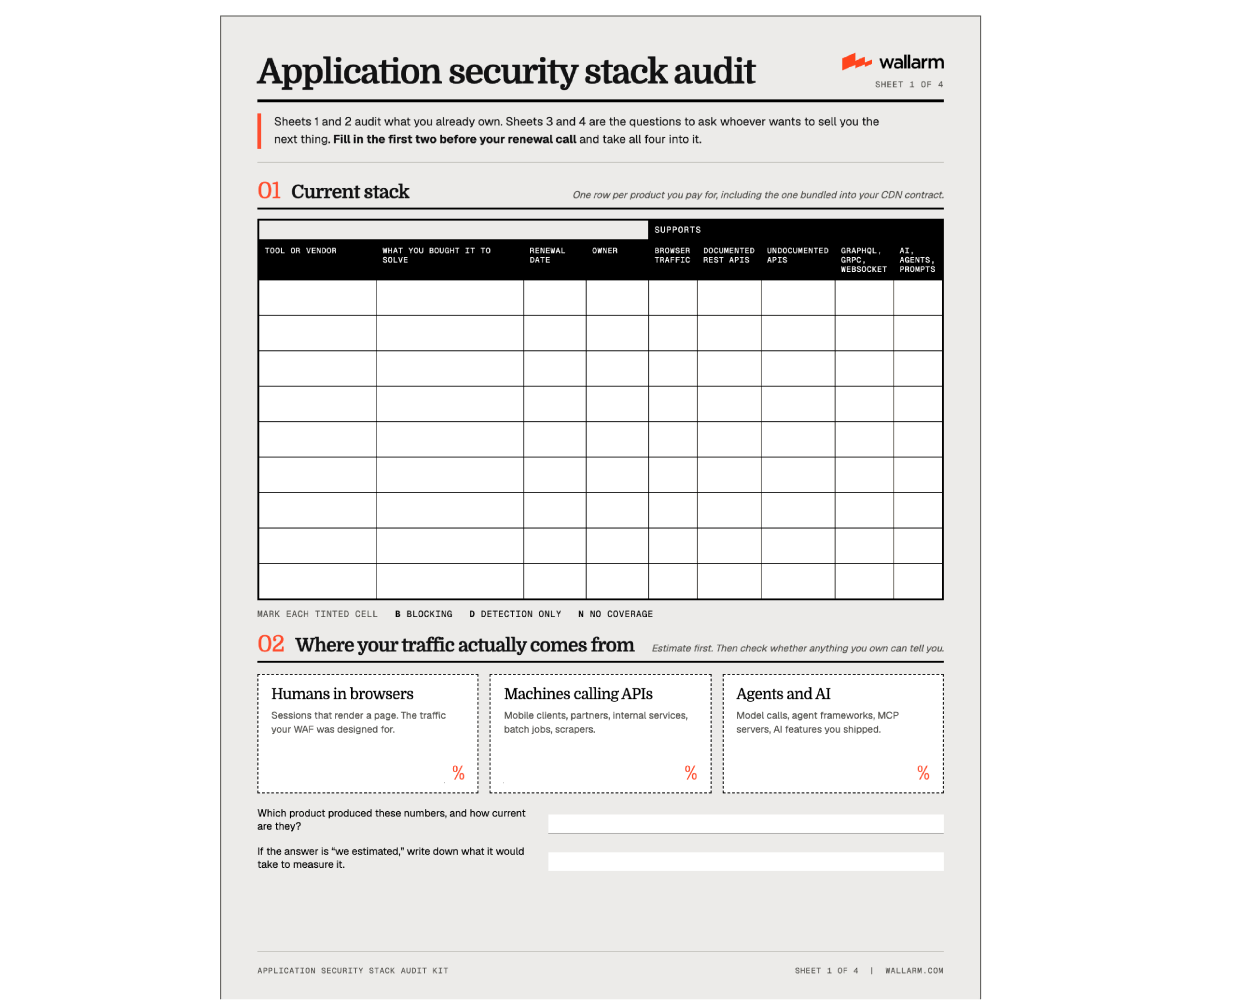
You're paying for tools that were built to watch humans in browsers. An increasing share of your traffic is APIs nobody documented, and now agents nobody approved. This kit is the worksheet version of that mismatch: four sheets to fill in before you talk to your current vendor, or the next one.
What's inside
- Current stack: one row per tool you pay for, what you bought it to solve, and whether it covers browser traffic, documented APIs, undocumented APIs, GraphQL/gRPC/WebSocket, and AI/agent traffic
- Where the gaps are: score your coverage 0–10 across five traffic types, then mark which team actually owns Discover, Observe, Enforce, and Govern for each
- Twelve questions to ask any WAF, WAAP, API, or AI security vendor, each with the answer that holds up, the one that sounds like an answer, and the one that's a red flag
Who it's for: AppSec, platform/SRE, and security leaders heading into a renewal, RFP, or budget conversation and want evidence in hand, not a vendor's word for it.
Trusted By
The world's most demanding teams run on Wallarm.


Ready to protect your APIs?
Wallarm helps you develop fast and stay secure.